
Description
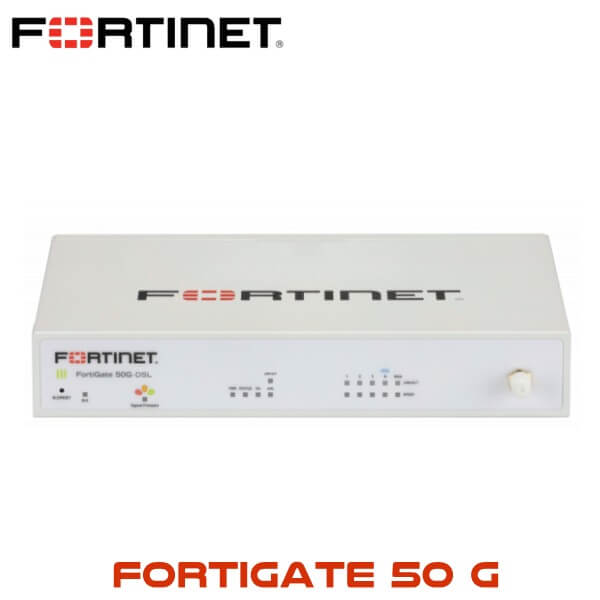
Fortigate50G Firewall Oman
The Fortigate50G Oman is an optimal solution for constructing security-driven networks across distributed enterprise locations and transforming WAN architecture at any scale. It is equipped with a comprehensive suite of AI and ML-driven FortiGuard security services, integrated within the Fortinet Security Fabric platform. This enables the Fortigate50G Oman to deliver coordinated, automated, and end-to-end threat protection across a diverse range of use cases. Notably, it features the industry’s first integrated SD-WAN and Zero Trust Network Access (ZTNA) enforcement within a Next-Generation Firewall (NGFW) solution, all powered by a unified operating system. The Fortigate50G efficiently controls, verifies, and facilitates user access to applications, ensuring a consistent and optimized user experience.
The Fortigate50G Oman is equipped with advanced features designed to enhance both network security and performance. Its NGFW provides comprehensive protection against a wide spectrum of cyber threats, including malware, viruses, spyware, and botnets. With SD-WAN capabilities, organizations can enjoy flexible and efficient WAN connectivity, optimizing network performance while minimizing costs. The device’s high-performance hardware, powered by Fortinet’s patented Security Fabric architecture, delivers superior security without compromising efficiency. Additionally, the AI-driven security system employs artificial intelligence to detect and neutralize advanced threats in real-time. The intuitive web-based interface simplifies configuration and management, while the device’s scalability ensures it can adapt to growing network demands. For distributed networks, the Fortigate50G Oman also supports cloud-based centralized management and monitoring, providing a streamlined solution for contemporary network requirements.
Models:
- Fortigate50G DSL
- Fortigate50G SFP
- Fortigate50G SFP POE
Specifications:
| System Performance — Enterprise Traffic Mix | |
| IPS Throughput | 2.25 Gbps |
| NGFW Throughput | 1.25 Gbps |
| Threat Protection Throughput | 1.1 Gbps |
| System Performance | |
| Firewall Throughput (1518 / 512 / 64 byte UDP packets) | 5 / 5 / 4 Gbps |
| Firewall Latency (64 byte UDP packets) | 2.42 μs |
| Firewall Throughput (Packets Per Second) | 6 Mpps |
| Concurrent Sessions (TCP) | 720 000 |
| New Sessions/Second (TCP) | 85 000 |
| Firewall Policies | 2000 |
| IPsec VPN Throughput (512 byte) | 4.5 Gbps |
| Gateway-to-Gateway IPsec VPN Tunnels | 200 |
| Client-to-Gateway IPsec VPN Tunnels | 250 |
| SSL-VPN Throughput | — |
| Concurrent SSL-VPN Users (Recommended Maximum, Tunnel Mode) | — |
| SSL Inspection Throughput (IPS, avg. HTTPS) | 1.3 Gbps |
| SSL Inspection CPS (IPS, avg. HTTPS) | 699 |
| SSL Inspection Concurrent Session (IPS, avg. HTTPS) | 74,000 |
| Application Control Throughput (HTTP 64K) | 2.8 Gbps |
| CAPWAP Throughput (HTTP 64K) | 3.8 Gbps |
| Virtual Domains (Default / Maximum) | 5/5 |
| Maximum Number of FortiSwitches Supported | 8 |
| Maximum Number of FortiAPs (Total / Tunnel Mode) | 16 / 8 |
| Maximum Number of FortiTokens | 500 |
| High Availability Configurations | Active-Active, Active-Passive, Clustering |